← December change on the Microsoft admin roadmap
Find the sending accounts
Imagine a branch scanner stops emailing PDFs. You need the account it uses, the person who manages it and one way to prove the fix. Exchange can give you the first lead.
- Open the Exchange admin center with access to mail flow reports. Microsoft lists Security Reader among the permitted roles.
- Go to Reports → Mail flow → SMTP AUTH clients report. Find the table headed Messages sent using SMTP AUTH.
- Record the observation date and the selected period. Start with seven days. Widen the period to include infrequent jobs, up to 90 days, and check any active filters.
- Read Sender Address and Authentication Protocol together. For a larger list, export the displayed rows to CSV and filter that column in your working copy. Keep the export in your internal support system.
What our tenant showed
On 10 November 2026, the default seven-day view returned zero rows. We changed the period to 90 days and waited for the table to reload. The count was still zero.
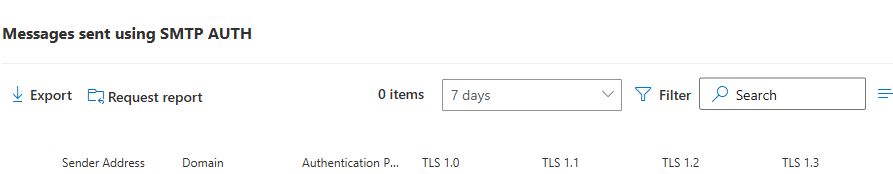
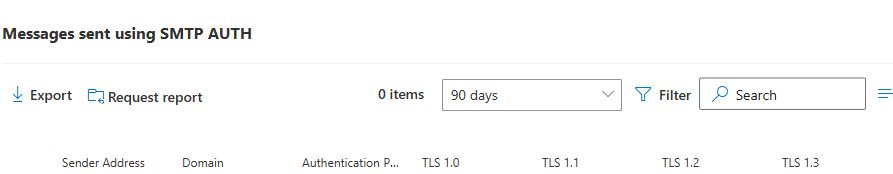
Ticket note. “No SMTP AUTH submissions were visible in either period reviewed. Device and application owners still need to account for other sending routes and jobs that ran outside the window.”
What does your result tell you?
Choose the outcome you see. TLS percentages describe the encrypted connection. The authentication column tells you whether a submission used Basic authentication or OAuth.
Basic Auth or TlsAuthLogin
Record the sender and period. Someone submitted mail using Basic authentication as that account. Check which systems hold its configuration. One account can serve several devices.
Modern Auth or XOAUTH2
Those submissions used OAuth. Check the remaining rows for Basic Auth, including rows for the same address. A successful OAuth submission confirms only that sending path.
The table is empty
Check the period and filters, then compare the result with the device inventory and job schedules. A copier using a connector-based relay, or an application using Microsoft Graph, follows a different mail path. If you know a device sent mail, inspect its configured destination with its owner.
Identify the device or scheduled job
Worked example · fictional sender
Suppose the report lists scan-office@example.org with Basic Auth. Two branch copiers use this account. The address gives you two candidates. The device name still needs confirmation.
Ask each owner to check the configured SMTP host and username in the copier or job settings. Record the asset name, owner and schedule. For a shared account, arrange a harmless test from one asset to an approved test mailbox. Give the message a unique subject and record the time and time zone.
Match the test to the device or job log and to the received message or Exchange message trace. The device log ties the send to the asset. The trace helps establish routing and delivery. Use protocol evidence separately when deciding how the client authenticated.
Retest before closing the ticket
If the client supports OAuth, pilot that configuration on one asset. For a device that cannot use OAuth, review Microsoft’s supported sending options against its network and recipient requirements. For example, a workflow that sends to external recipients cannot use Direct Send to reach them.
- Delivery. Record the test sender, recipient, time and successful receipt. Use a recipient representative of the real workflow.
- Authentication. For a sender moved to SMTP with OAuth, look for Modern Auth in a fresh reporting interval once the report updates. For a connector-based relay, verify the configured connector and delivery path separately.
- Handover. Record the sending asset, its owner, the replacement method and evidence from the next scheduled run. Keep other assets sharing the account open until tested.
The tenant exercise here stopped after reading the report. We observed no Basic Auth sender to migrate or retest.
Once you have identified an affected sender, choose its migration path and verify delivery with the workload owner.
Microsoft sources
- Exchange Team · December default change and final retirement timeline
- Microsoft Learn · SMTP AUTH Clients report, fields and observation window
- Microsoft Learn · Roles for mail flow reports
- Microsoft Learn · Tenant and mailbox SMTP AUTH settings
- Microsoft Learn · Sending options for devices and applications